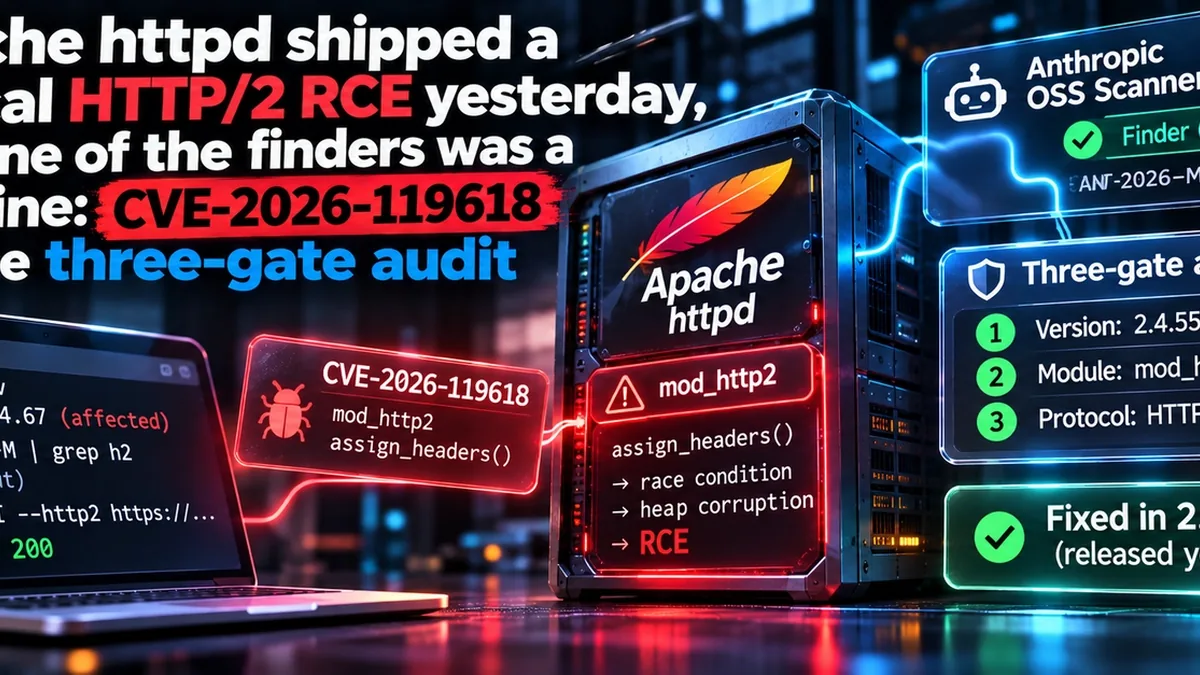
Apache httpd shipped a critical HTTP/2 RCE yesterday, and one of the finders was a machine: CVE-2026-119618 and the three-gate audit
8.9 relevance
Score Breakdown
technical depth 9
novelty 9
actionability 9
community 8
strategic 9
personal 9
Scored daily by a customisable AI persona to surface the most relevant engineering leadership news.
Critical security vulnerability found by AI scanner, highly actionable and strategically important.
Summary
Apache httpd 2.4.71 patches CVE-2026-119618, a critical HTTP/2 RCE from a race condition in mod_http2's assign_headers() affecting versions 2.4.55–2.4.70. Wiz telemetry shows 64% of cloud environments have a vulnerable instance, 51% publicly exposed. Notably, Anthropic's OSS Scanner—previously criticized for 56% false-positive rate—was the first finder, demonstrating that high-noise AI tools can still deliver high-signal security findings.