Universal XSS in uBlock Origin from website-driven element picker
Scored daily by a customisable AI persona to surface the most relevant engineering leadership news.
Security vulnerability in uBlock Origin with technical depth, actionable for developers using the extension.
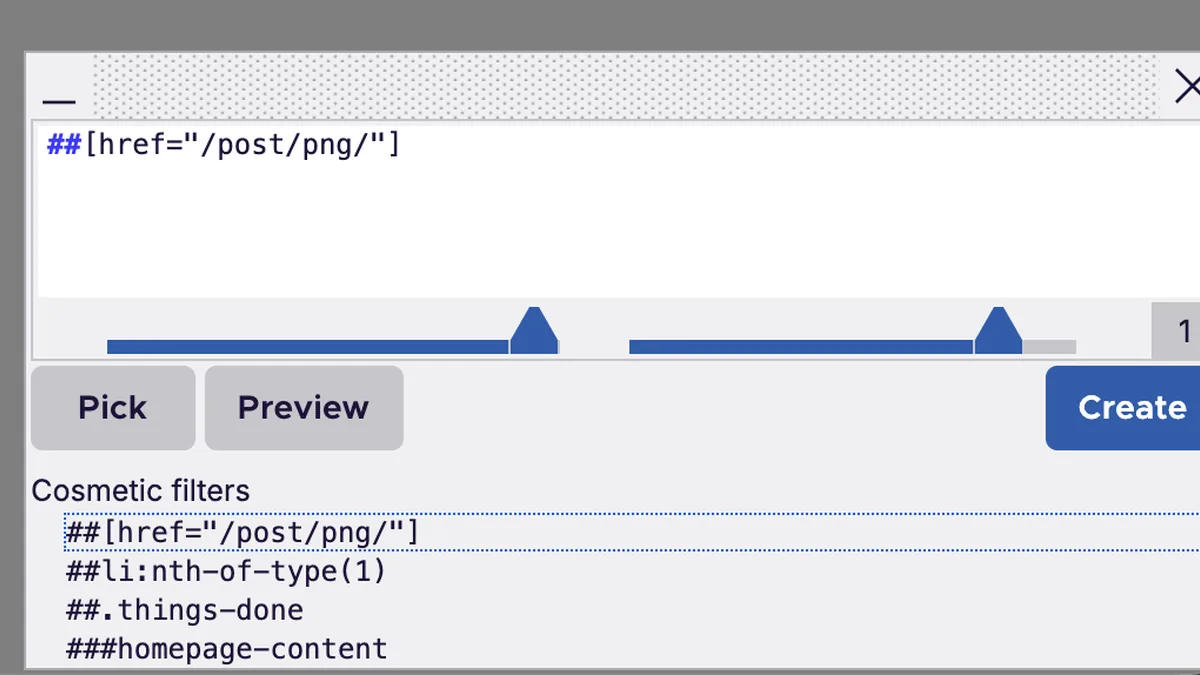
A universal XSS vulnerability in uBlock Origin (MV2 Firefox version) allowed malicious websites to extract the extension's internal UUID by hooking XHR calls made from the no-fetch-if filter rule, then embed an invisible element picker iframe to trick users into creating arbitrary trusted filters that execute JavaScript in any site context. The attack chain involves leaking the UUID via fetch hook interception, driving the picker via postMessage with crafted opt fields containing newlines to bypass filter restrictions, and positioning the invisible iframe to capture user clicks on the Create button. The issue is fixed, with GPT-5.6 Sol credited for finding the vulnerability and Claude for generating the proof-of-concept code.