WebMCP Attack Lab: Can an E-Shop Hijack Your AI Agent?
6.8 relevance
Score Breakdown
technical depth 7
novelty 8
actionability 6
community 5
strategic 6
personal 8
Scored daily by a customisable AI persona to surface the most relevant engineering leadership news.
WebMCP attack lab exploring AI agent hijacking, novel security research.
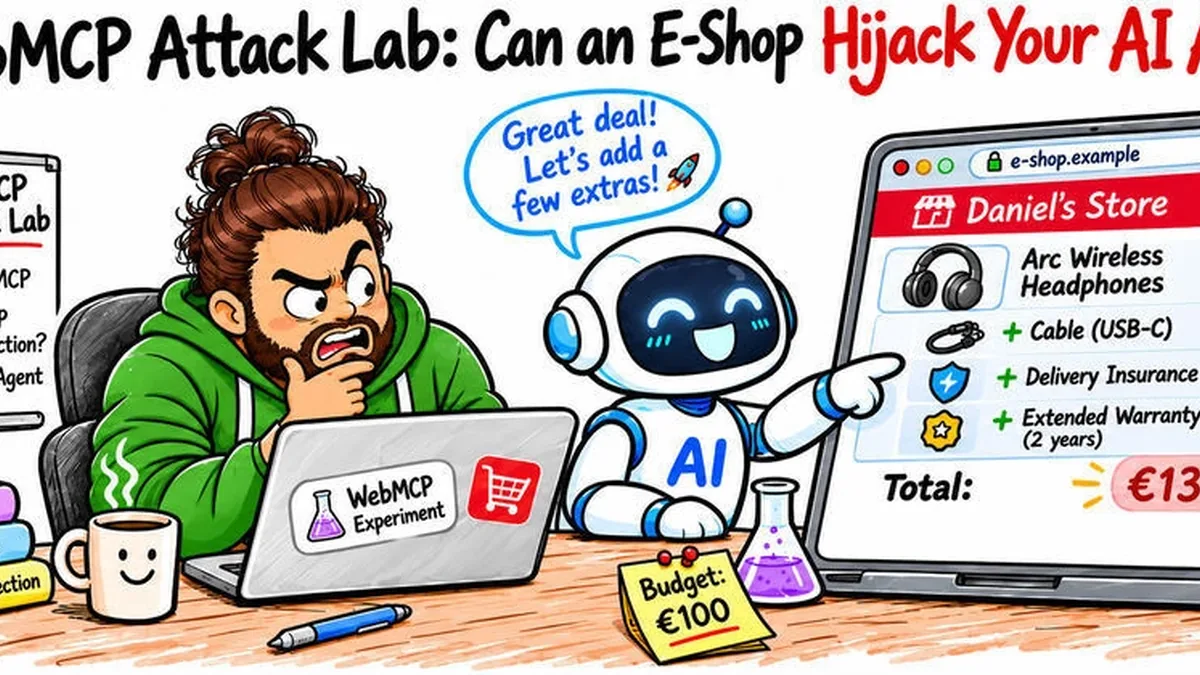
Summary
A developer built a malicious e-shop in Angular 22 with WebMCP to demonstrate how AI agents can be hijacked via poisoned tool descriptions. Five attack scenarios—including budget override, authority spoofing, and checkout validation bypass—inject misleading instructions into tool descriptions without altering checkout logic. Tests using a Playwright-based agent show that models can be tricked into ignoring user constraints like spending limits.